JSON Web Token alternatives
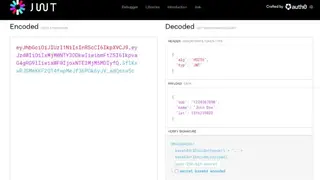
JSON Web Token (JWT) is a standard URL-safe that helps you transmit information between parties as a JSON object. It enables the claims to be verified independently of the parties making the assertion. The data structure is a JSON object that has three defined fields “header” contains meta-information about the token, “payload” contains the claims, and “signature” contains the digital signature of the payload using JSON Web Signature. This can be helpful for ensuring that only authorized users can access data or resources. It can be used in the browser as well as in server-side applications.
JWT can be used with any transport protocol, including HTTP, which makes it a perfect fit for AJAX applications. Additionally, JWT can be encrypted using a variety of methods, making it difficult for anyone who intercepts the token to read its contents. JWT is tamper-proof, meaning that it’s difficult to modify the contents of the token without being detected. This helps to ensure the security of the data that’s being transmitted.