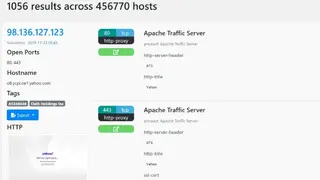
IVRE is an open-source framework for network penetration. It gathers data from network intelligence, stores it in the database, and provides tools to analyze it. MongoDB is recommended for maximum reliability. The web interface allows you to analyze Nmap scan results, and due to the fact that it relies on a database, it can be much more efficient with huge scans than a tool like Zenmap. The easy-to-use interface lets you browse network flows with ease. It lets you import the results from Zeek, Argus, or Net flow, and the data can be explored from a CLI and Python API.
After getting the results, you can process it with your favorite analysis tools lie RT Graph and matplotlib. Additionally, you can also filter, have quick access to previous results for a specific host, and look for specific services or vulnerable versions within a specific country or network, etc. IVRE includes tools to run Nmap against targets like a network or an address range, a whole country, a specific AS, or the full IPv4 connected address space.