RSA NetWitness Logs and Packets (RSA SIEM) alternatives
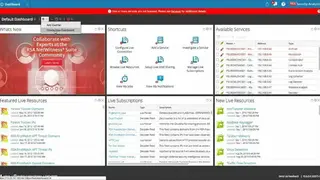
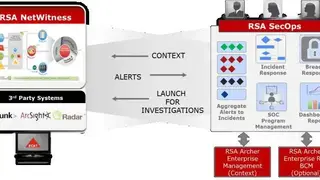
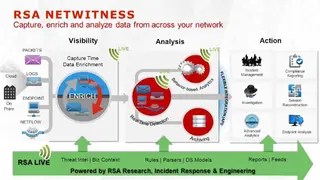
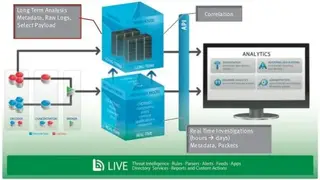
RSA NetWitness Logs and Packets (RSA SIEM) is an all-in-one security information and event management solution that helps security teams easily detect all kinds of cyber threats and accelerate incident response. The solution is uniquely created for all businesses and organizations to protect all valuable digital assets. It collects and analyzes logs, NetFlow, network packets, and endpoint data. All these capabilities allow organizations to quickly discover attacks that traditional log-centric security information and event management miss.
At the time of the collection, it uses capture time data enrichment to inspect every piece of data gathered for threat indicators. The best part about this solution is investigating threats in just a minute instead of hours or days. RSA NetWitness Logs and Packets (RSA SIEM) other prominent feature includes gain visibility. It correlates across logs, endpoints, and networks, uses behavior analytics, focuses on the most important event, streamlines security analyst workflow with a single tool, etc. It is a commercial solution with different price plans; each plan has its own cost and core benefits.