Home Network & Admin Security & Privacy
Splunk Enterprise SIEM alternatives
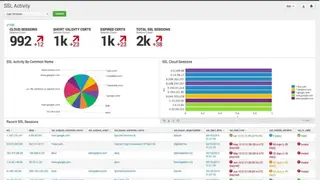
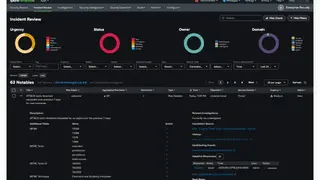
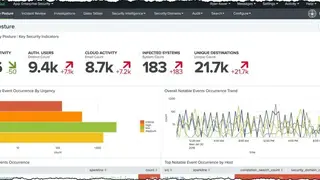
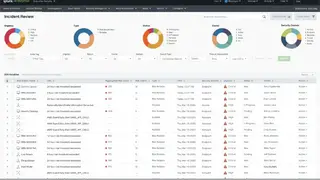
Splunk Enterprise SIEM is a cloud-based, analytics-driven security information and event management platform that provides real-time visibility into security events, end-user behaviors, IT infrastructure utilization, and operational status. It enables you to detect and respond to advanced threats and data breaches by collecting, analyzing, and acting on machine data in real-time. The platform features a wide range of security analytics and threat detection capabilities that enable customers to capture, index, search and monitor their large volumes of security-related events.
Splunk’s machine data analytics capabilities are paired with its search capabilities, user interface enhancements, REST API, and open app ecosystem to provide a complete platform. Its analysis of machine data and log files can surface malicious activity and trigger automated responses, significantly improving response time against attacks. All in all, Splunk Enterprise SIEM is a great solution that you can consider among its alternatives.